SaaS Alerts to Software Companies: Give Us More Data

SaaS Alerts to Software Companies: Give Us More Data

SaaS applications have become the most dangerous and widespread threat vector for businesses of all sizes. A key issue in keeping them secure is that many software companies DO NOT include security log data in their APIs, which inhibits user behavior monitoring inside those applications.

SaaS Alerts is circulating a petition — it isn’t clear to who — to ask software companies to include security log data in their APIs. This is, in some ways, an odd petition. Very few people want to directly consume this type of data unless they already run a SIEM or syslog server, in which case they typically expect the data in a format their SIEM or syslog can already ingest.

I understand the petition as asking for a Restful API (although I expect SaaS Alerts would use a syslog feed if that was all that was available). I’ll assume that SaaS Alerts would like the ability to have events pushed (i.e., webhooks) and searchable. It’s what I’d want.

At its most basic, this is a petition to give SaaS Alerts more business — which is fine by me; JM Addington Technology Solutions was their 4th customer as we love working with them. Beyond that there are a lot of reasons to like the idea.

First, the security events for most SaaS applications are completely opaque. Vendors like Intuit, Keap, Zoom, Huntress, and most Kaseya products do not offer much — if any — visibility into IAM events that take place. You don’t know if there are unsuccessful logins (unless you are locked out), who accessed what and when, or deleted something, or created something, or created a new user, and so on. The SaaS Alerts petition is a request to change this, to ask these vendors to give us visibility into the security events on the platforms we use every day.

The second reason I like the idea is that it greatly expands the services MSPs like mine can offer to clients. I think it would be a huge win to be able to offer monitoring — and remediation — for SaaS products. Security around their entire data perimeter.

Third, it would let us build out a new class of products. Today, JM Addington Technology Solutions and CyberSecureRIA have built a custom reporting and compliance tool that includes reporting for M365 and G Suite, two platforms that do have security log data in their APIs. I would absolutely love to expand that to a broader range of products.

Finally, it would add accountability. With no transparency into the inner workings of most SaaS applications, we have to pray and hope that platforms are not only protecting their infrastructure but our own tenants as well.

Why an API and Not Syslog?

Because JSON APIs are easily consumable today. All modern programming languages support them, often nativeily. Syslogs are also one way, you either consumed it at the time the info was sent or you lost it. The ability to search and request items that were not successfully sent is helpful.

Report: no reason to fire Sam Altman

Report: no reason to fire Sam Altman

Ars Technica

After reportedly interviewing dozens of people and reviewing over 30,000 documents, [the legal firm hired to investigate Altman’s firing] found that while the prior board acted within its purview, Altman’s termination was unwarranted. “WilmerHale found that the prior Board acted within its broad discretion to terminate Mr. Altman,” OpenAI wrote, “but also found that his conduct did not mandate removal.”

I am neutral on Sam Altman as a whole. I think that this episode is a net—negative for keeping AI development in check — especially at Open AI, as Sam Altman now essentially seems invincible.

Lead Gas Lowered Americans’ IQ

Lead Gas Lowered Americans’ IQ

I wish NBC News had linked to the study-and that I had time to read it even if had. It sounds interesting, and at the same time, incredible that they are able to make such an estimate.

Story

The peer-reviewed study, published Monday in the journal Proceedings of the National Academy of Sciences, focuses on people born before 1996 — the year the U.S. banned gas containing lead.

Exposure to leaded gasoline lowered the IQ of about half the population of the United States, a new study estimates.

Overall, the researchers from Florida State University and Duke University found, childhood lead exposure cost America an estimated 824 million points, or 2.6 points per person on average. 

Polsko, dlaczego tu jesteś?

Polsko, dlaczego tu jesteś?

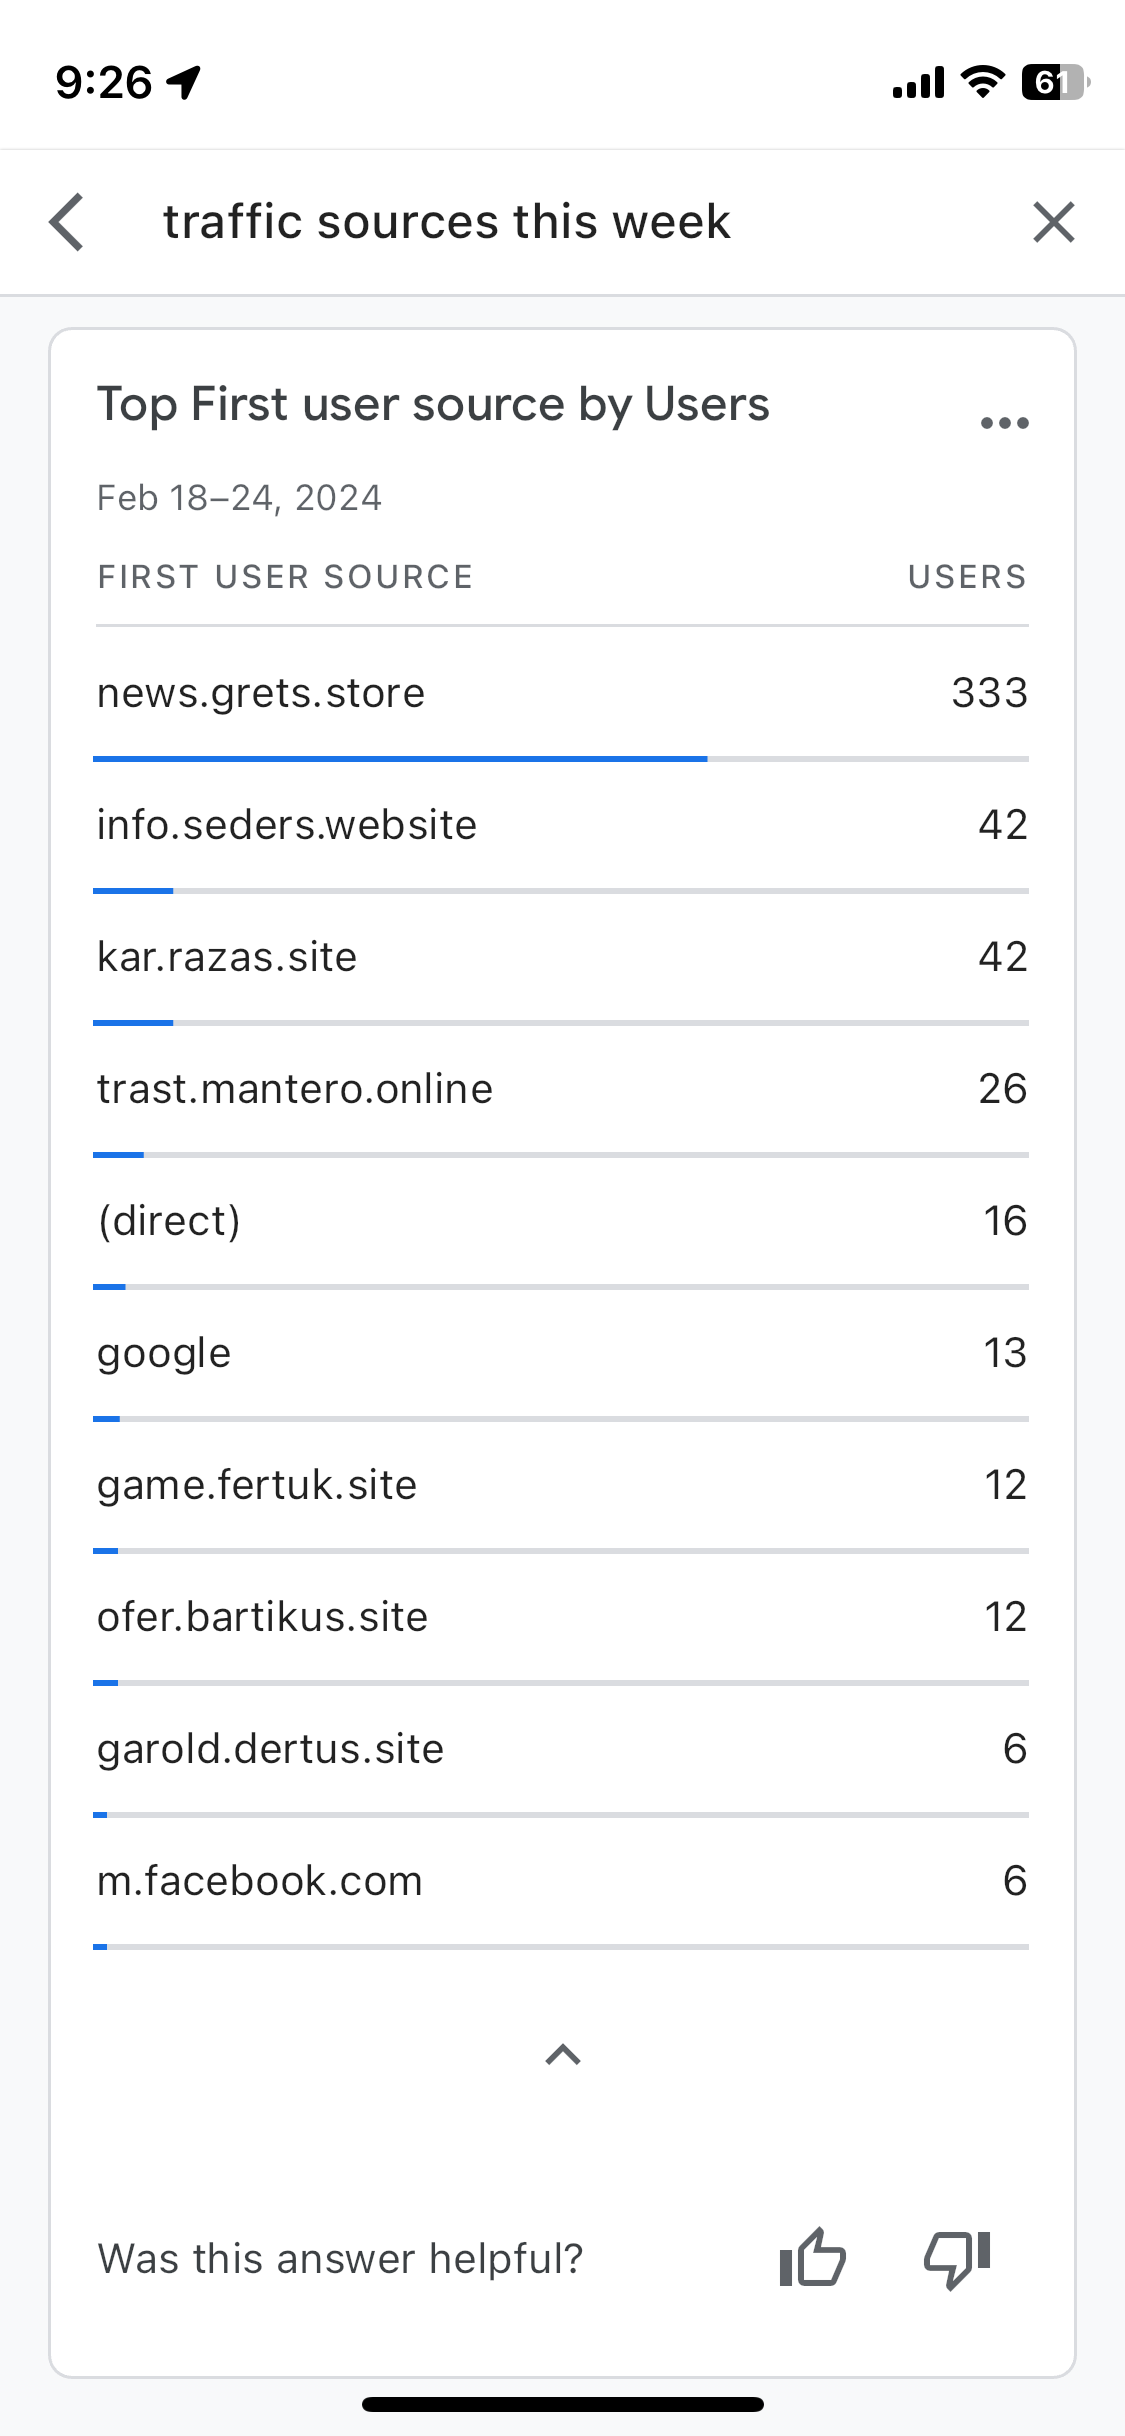
I really don’t understand all my Polish visitors. The top referring source looks like a hacked site.

If you have any insights for me drop a comment or find me on social media to let me know.

It’s also possible I get a different website from a North American IP than I would from a European IP, but I don’t readily have a way to test.

Poland Visitors, This Is Not The Site You Are Looking For

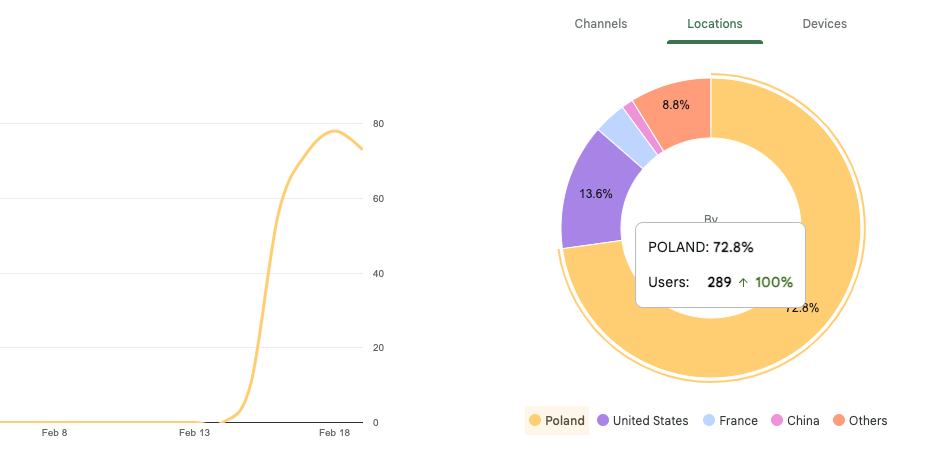
Since 16 Feb 2024 the vast majority of visitors are from Poland, and they are all referrals.

If you don’t know how you got here, you probably don’t actually want to be here.

This image contains two data visualizations related to website visitors from Poland. On the left, there is a line graph showing a sharp increase in the number of visitors over time, starting from February 8th and peaking around February 18th. On the right, there is a donut chart displaying the percentage of visitors by country, with Poland accounting for 72.8% of the traffic, which is the largest share. The chart indicates that there are 289 users from Poland, marking a 100% increase. Other countries represented in smaller percentages are the United States, France, China, and a category labeled as Others. The colors corresponding to each country are indicated at the bottom: Poland is yellow, United States is blue, France is purple, China is green, and Others is gray. The chart segments are also labeled with their respective percentages.

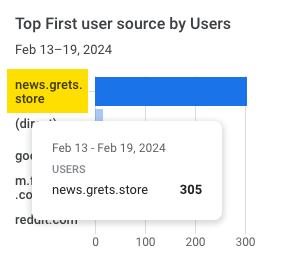
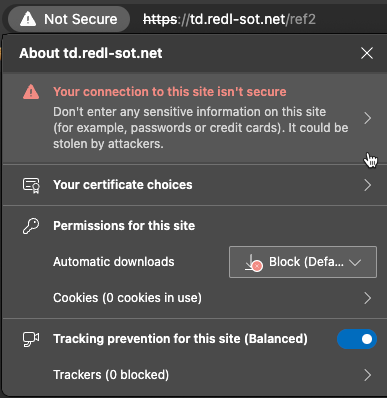
The referring site is news.grets.store, which redirects to another site, td.redl-sot.net

And that site has an invalid TLS cert, and is blocked by my firewall as a phishing site.

Bar chart showing 'Top First user source by Users' for the week of February 13-19, 2024. The highest referrer is 'news.grets.store' with 305 users, highlighted in blue on the chart.
Browser security warning indicating the connection to the site 'td.redl-sot.net' is not secure, advising not to enter sensitive information as it could be stolen by attackers. Options for certificate choices, site permissions, automatic downloads, cookies, and tracking prevention are shown. Tracking prevention is set to 'Balanced' with zero trackers blocked.

All of which is pretty odd, unless my site is serving up malware, which would be unexpected. Not because WordPress is great at security, but I use FlyWheel and CloudFlare, both of which I’d expect to catch any malware on the site.

Google also isn’t flagging this site as malicious, which it is typically quick to do.

Posts in This Category